
Short answer
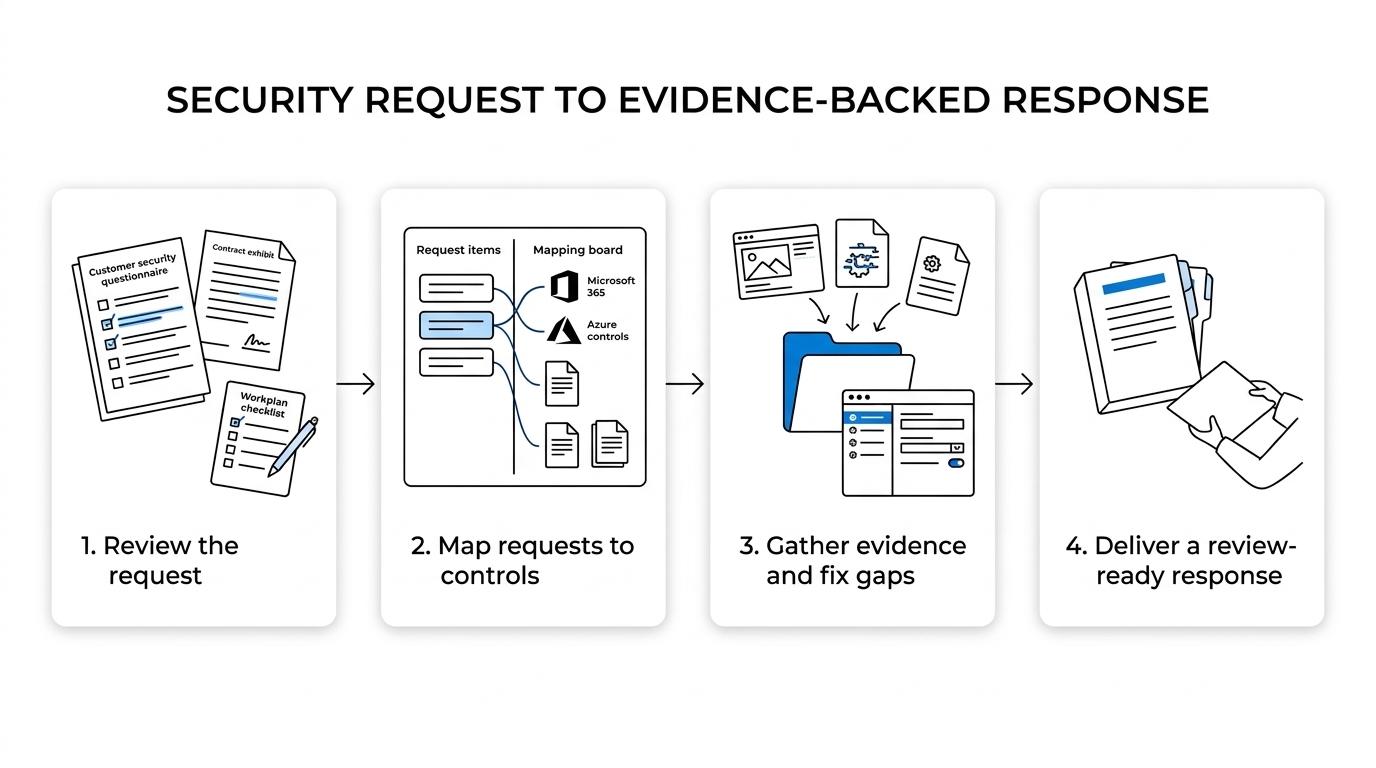
Vendor security assessment help means answering a customer questionnaire, supplier due diligence review or contract security exhibit with evidence rather than assurances. Ethereum Tech maps each request to your existing Microsoft 365 and Azure controls, finds the gaps, collects the screenshots, settings and policies that prove each answer, and helps configure missing controls before customers, primes, insurers or auditors follow up.
Check where you stand: take the SOC 2 and ISO 27001 check. About two minutes, no email needed.
When a customer, prime contractor, insurer, or procurement team asks you to complete a security questionnaire, supplier due diligence review, contract security exhibit, or deeper evidence request, Ethereum Tech LLC helps organizations using Microsoft 365 and Azure respond with documented evidence, control mapping, and hands on security and compliance support that stands up to follow up questions.
If your team is facing a security questionnaire, supplier due diligence review, contract security exhibit, or deeper evidence request, Ethereum Tech helps you turn that request into a clear workplan. We help you identify what is being asked, gather the right artifacts, configure missing controls where needed, and prepare for independent review instead of relying on self attestation alone.
Vendor security assessment response support for Microsoft 365 and Azure environments
Vendor security assessments often mix contract language, framework references, technical questions, and evidence requests into one deadline driven process. Ethereum Tech provides vendor security assessment response help for Microsoft 365 and Azure organizations by translating those requests into concrete tasks, evidence collection, and remediation steps so your response is clearer, faster, and more defensible.
What you get depends on the request in front of you, but our support typically includes:
- Review of customer questionnaires, security exhibits, due diligence forms, or portal submissions
- Mapping of requests to your existing Microsoft 365 and Azure controls, policies, and documentation
- Identification of gaps that may affect the response, audit readiness, or contract acceptance
- Evidence collection support for screenshots, settings, policies, procedures, and supporting records
- Hands on configuration help when security or compliance controls need to be implemented or improved
- Preparation for follow up from customer security teams, independent assessors, or auditors
Ethereum Tech builds the response around the real trigger you have today, whether that is a new customer review, renewal, leadership request, cyber insurance evidence request, or a larger compliance initiative already underway.
Ethereum Tech helps defense contractors, healthcare vendors, and teams under customer security review
Some vendor assessments are lightweight. Others quickly expand into CMMC, NIST, HIPAA, HITRUST, SOC 2, ISO 27001, or cyber insurance evidence questions. Ethereum Tech helps defense contractors, healthcare related organizations, and companies answering customer security requirements connect those requests to the Microsoft 365 and Azure controls they actually use.
Ethereum Tech supports CMMC Level 1 and 2 readiness alongside broader NIST, HIPAA, HITRUST, SOC 2, and ISO 27001 readiness needs.
That matters when your customer is not just asking whether a control exists, but how it is configured, who manages it, what evidence supports it, and how exceptions are handled. We help you respond in a way that reflects your real environment and your real obligations.
Ethereum Tech also works alongside internal IT teams and MSPs. You do not need to replace your current technical team to get vendor assessment support that is organized, technically grounded, and ready for customer review.
Evidence first vendor security assessment help aligned to current due diligence expectations
Current guidance has moved well past simple vendor assurances. NIST SP 1326, a quick start guide NIST finalized in July 2026, organizes supplier due diligence around five areas: foreign ownership, control or influence (FOCI), provenance, resilience, foundational cyber practices and supply chain tiers. Ethereum Tech helps you prepare documented evidence and response support that fits this more structured review model, especially when a customer wants more than a checkbox answer.
Ethereum Tech helps you move beyond self attestation by organizing documented controls, artifacts, and assessment ready evidence.
That approach also fits broader federal expectations. FTC guidance for businesses under the Safeguards Rule asks them to choose capable service providers, spell out security expectations in contracts and reassess providers over time. NIST supply chain guidance treats supplier review as ongoing work. The Cybersecurity Framework 2.0 calls for due diligence before a supplier relationship starts and for monitoring supplier risk over the course of the relationship (GV.SC-06 and GV.SC-07), and NIST SP 800-161 Rev. 1 builds that review into documented policies, plans and risk assessments. Ethereum Tech uses those realities to shape stronger responses when your customer expects proof, not just promises.
For you, that means less scrambling to explain your environment at the last minute. We help organize the artifacts, settings, policies, and supporting documentation that make your response easier for a customer security reviewer, assessor, or auditor to evaluate.
Ethereum Tech combines vendor questionnaire support with hands on Microsoft 365 and Azure remediation
Many firms will help draft answers. Ethereum Tech goes further by supporting the technical work behind the answers when your Microsoft 365 or Azure environment needs improvement. If your questionnaire response exposes missing controls, weak documentation, or incomplete evidence, we can help address those issues directly.
This is where our Microsoft 365 and Azure specialization becomes practical. Ethereum Tech helps collect evidence, support compliance configuration, and align technical settings with the security and compliance commitments your organization is making in a vendor assessment response.
That usually improves more than the questionnaire itself. You can reduce rework, avoid inconsistent answers across customers, and build a stronger foundation for future audits, insurance renewals, and internal security initiatives.
Here is what becomes easier when Ethereum Tech is involved early:
- Your customer facing answers are tied to real controls and real evidence
- Your IT team has a clearer list of what must be configured, documented, or remediated
- Your leadership team gets a more accurate picture of current risk and response readiness
- Your organization is better prepared for independent assessors, auditors, and repeat reviews
Vendor security assessment response with Ethereum Tech is a strong fit when proof matters
Ethereum Tech is a strong fit when the assessment is not just a formality and the stakes are commercial, contractual, or regulatory. We are especially useful when the response depends on Microsoft 365 or Azure evidence, when a customer is asking deeper control questions, or when your team needs both compliance guidance and technical follow through.
You are likely a good fit for Ethereum Tech if:
- You need help answering a customer or procurement security questionnaire tied to Microsoft 365 or Azure
- A prime contractor or enterprise customer is asking for stronger evidence, not just policy statements
- Your organization is preparing for CMMC, NIST, HIPAA, HITRUST, SOC 2, or ISO 27001 readiness and customer reviews are arriving before that work is finished
- You need outside support that can work alongside your internal IT team or MSP
- You want assessment ready documentation that can be reused for future audits, renewals, or vendor reviews
If you only need a generic template response, we may not be the right choice. Ethereum Tech is built for organizations that need vendor security assessment help connected to real systems, real evidence, and real implementation work.
Send Ethereum Tech your vendor security questionnaire, contract, or evidence request
The fastest way to start is with the actual request. Send Ethereum Tech the customer questionnaire, contract language, security addendum, portal requirements, or evidence list you need to answer, and we will help you determine what is already covered, what is missing, and what should happen next in Microsoft 365 and Azure.
That gives you a clearer path to a credible vendor security assessment response, stronger evidence for customer review, and less risk of overcommitting to controls that are not yet in place. Book a 30 minute call to turn the assessment in front of you into a practical plan your team can execute.
Frequently asked questions
What evidence do customers usually ask for in a vendor security assessment?
Most requests ask for written policies, screenshots or exports of security settings, and records that show a control is actually operating, such as MFA enforcement or access reviews. In a Microsoft 365 or Azure environment most of that comes from your own tenant, so export it with a date instead of describing it.
What is NIST SP 1326?
NIST SP 1326 is a NIST quick start guide for cybersecurity supply chain due diligence assessments, published in final form in July 2026. It organizes supplier due diligence around five areas: foreign ownership, control or influence (FOCI), provenance, resilience, foundational cyber practices and supply chain tiers.
How does the FTC Safeguards Rule affect vendor reviews?
Businesses covered by the rule must select service providers that can maintain appropriate safeguards, require those safeguards by contract and periodically reassess providers based on the risk they present. If your customer is covered, expect security terms in your contract and repeat reviews over the life of the relationship.
What if a questionnaire asks about a control we do not have yet?
Answer accurately by stating what is in place, what is missing and what you plan to do, rather than claiming a control you cannot show. Ethereum Tech helps configure the missing control in Microsoft 365 or Azure and collects the evidence once it is working.
Do you replace our internal IT team or MSP?
No, we work alongside your internal IT team or MSP and do not take over the environment. We map requests to controls, collect evidence and help configure missing controls, while your team keeps running daily operations and owns the systems.